
Your patient data,
under your control
Most AI tools route patient data through third-party language models. Vascue handles raw patient data on self-hosted infrastructure and masks identifiers before any content is passed onward, all under ISO 27001, so confidentiality is the default, not a setting.
- Self-hosted
- /
- PII masked
- /
- ISO 27001
- /
- No data selling
Privacy built into the architecture
Not a policy bolted on afterwards. The way the system is built is the way it keeps data safe.
Self-hosted handling
The components that handle raw patient data run inside our controlled environment, not a third-party cloud.
Identifiers masked
Direct identifiers are masked at the boundary before any content is passed onward, so downstream models work on de-identified data.
No raw data to third parties
Raw patient data and direct identifiers are never sent to a third-party model. Only de-identified, minimised content is passed onward.
ISO 27001 certified
Independently audited information-security management, recertified on schedule.
No data selling
We never sell your data or train shared models on it.
Human override
Staff can take over any conversation at any time. The AI never locks you out.
At the privacy boundary
Patient message
WhatsApp, web, or other channels
Identifiers masked
Names, IDs, and contacts removed at the boundary
De-identified content processed
Only masked, minimised data continues onward
Raw patient data and direct identifiers never cross this boundary.
Questions reviewers ask us
- Where is patient data processed?
- The components that handle raw patient data run inside Vascue's controlled, self-hosted environment, not a third-party cloud. Direct identifiers are masked at the boundary, and only de-identified, minimised content is passed to any downstream model.
- Is Vascue ISO 27001 certified?
- Yes. Vascue Limited holds ISO/IEC 27001 certification for its information-security management system, independently audited and recertified on schedule. The certificate is published on this page and in the Trust Center.
- Can the AI submit insurance claims on its own?
- No. Vascue Claims prepares source-linked drafts and runs deterministic checks, but clinic staff authorise every submission and can review each claim before it leaves the clinic.
- Can staff take over a patient conversation?
- At any time. The AI front desk never locks staff out; any conversation can be picked up by a person, and it stays in the same thread the patient is already using.
- Do you sell data or train shared models on it?
- No. Vascue never sells customer or patient data and does not train shared models on it.
How this plays out in each product: the AI Front Desk keeps staff in every conversation, and Vascue Claims keeps the submit with your team. The Hong Kong radiology case study shows the architecture running at hospital volume.
How we think about safety
 Healthcare AI
Patient Communication AI in a Hong Kong Hospital: A Privacy-First Architecture on AWS
Inside the privacy-first AWS architecture Vascue built for a Hong Kong hospital radiology department, where patient data is de-identified on Vascue's own infrastructure before it ever reaches a hosted model.
5 min read Healthcare AI
Should AI Submit Insurance Claims Without Human Review?
A risk-based boundary for claims automation: what software can prepare, what staff should authorize, and why Vascue does not treat full autonomy as the default.
6 min read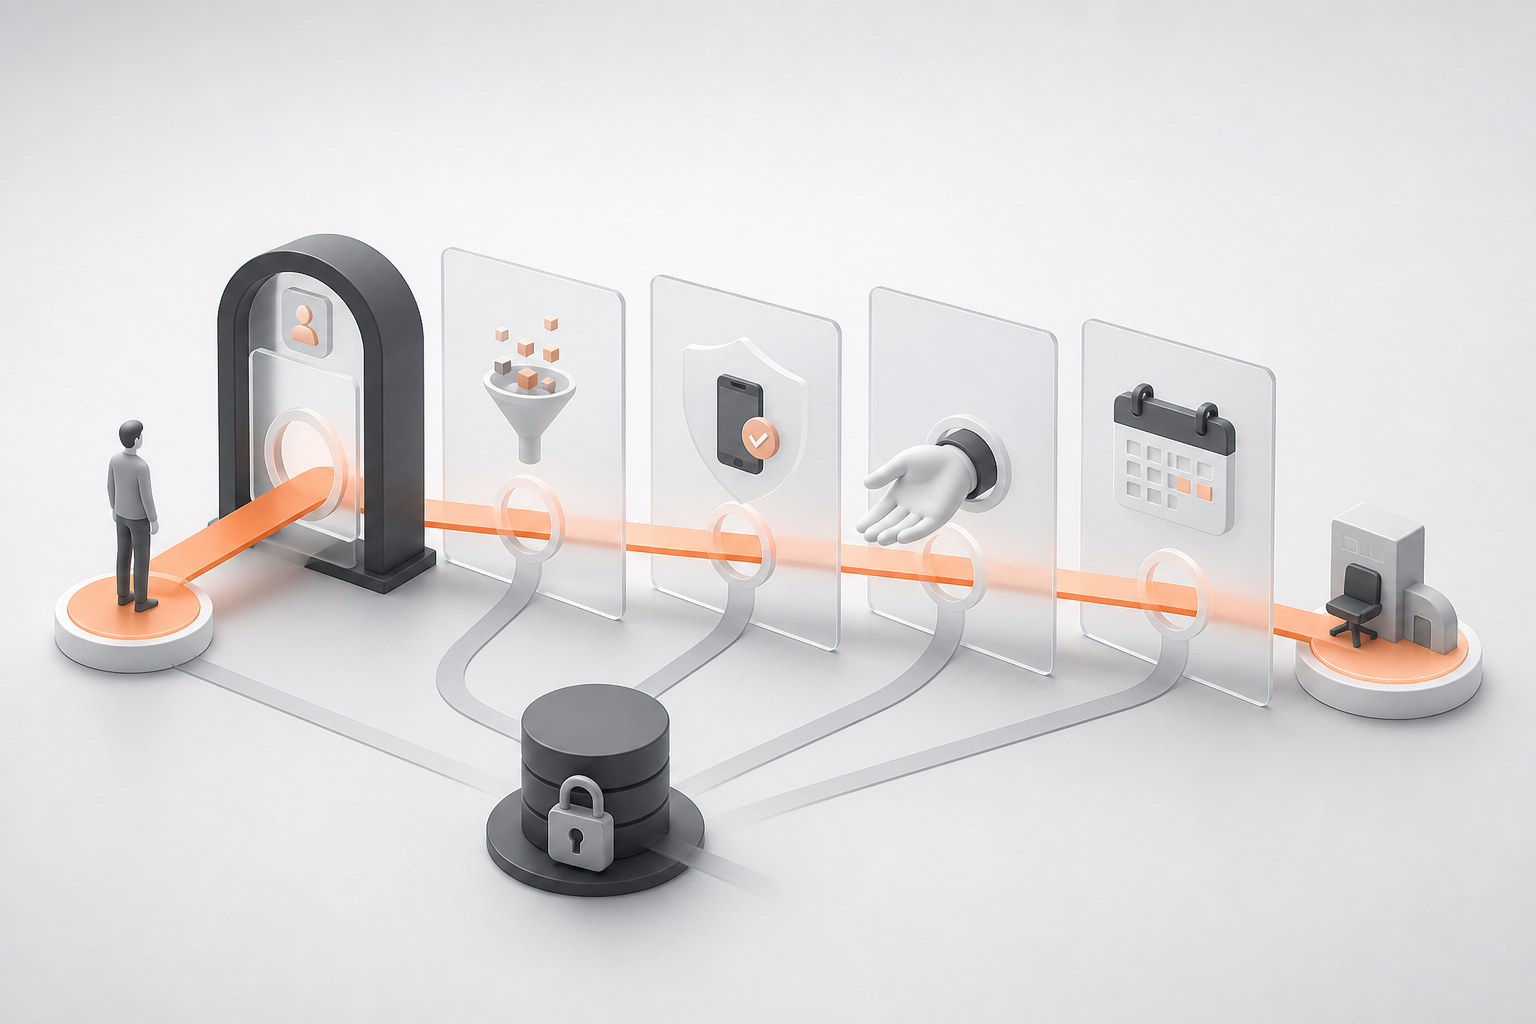 Healthcare AI
The Guardrails Behind AI Booking in Healthcare
AI booking should be an administrative assistant with clear limits, not an autonomous actor with broad access to healthcare systems.
5 min read


